Issue November 21Daily digest · 12 items
In this issueReviewed 23 sources, gathered 12 items
Brass padlock engraved with SESAME and a glowing green access key on a dark background
ArticleDevelopmentSafetyAI AgentsAdonisJS

@adonisjs/sesame: Built-in OAuth 2.1 and OpenID Connect Server for AdonisJS with MCP Agent Support

The AdonisJS team has released the official @adonisjs/sesame v0.11 package, a built-in OAuth 2.1 and OpenID Connect server for AdonisJS 7 and Node.js 24+. It leaves your user tables and login screens untouched while covering key security risks out of the box: mandatory PKCE, URL-spoofing protection on the consent screen, full grant revocation on refresh token theft, and auto-discovery for AI agents via MCP. We inspect the package code and test replay detection in an interactive demo.
👍 11
AdonisJS BlogGitHub: adonisjs/sesameAdonisJS Docs — OAuth Server (Sesame)
November 21
Stylized graphic poster showing a digital barrier and a 300 request rate-limit gauge in high-contrast tones
ArticleDevelopmentSafetyAWSDevOps

300 Requests in 5 Minutes: How Engineers Chose an AWS WAF Limit for the Token Route and Caught Their Own Bugs First

One stuck client sending 20 requests per second can exhaust all 30 AWS Lambda slots on a token route and take down auth for everyone else. In a real 16-day case study by SRE Daniil Romashov, we look at choosing an AWS WAF threshold from weekly CloudFront logs, working Terraform with a 429 response, a CloudWatch Alarm trap with the Rule dimension, a twin rule for the QA runner, and blocking direct API Gateway bypasses.

👍 18
DevOps&SRE LibraryHackerNoon — 300 Requests in 5 Minutes (Daniil Romashov)AWS WAF Developer Guide — Rate-based rule statements
November 21
Isometric 3D model of a powerful database server with extension slots and the blue PostgreSQL elephant
ArticleDevelopmentDataPostgreSQLArchitecture

Why Run Five Different Databases When PostgreSQL Already Does Almost Everything: JSONB, pgvector, Search, Metrics, and Queues

MongoDB for JSON, Pinecone for vectors, Elasticsearch for search, InfluxDB for metrics, and Redis for queues—this stack looks impressive on day one, then turns into five connection pools, separate backups, and 3 AM alerts six months later. Using working SQL examples, we show how a single PostgreSQL cluster with extensions covers 80–90% of those jobs, where pgvector and LISTEN/NOTIFY hit their limits, and when a separate database actually pays off.

👍 15
SQL PortalPostgreSQL Docs — JSON TypesGitHub: pgvector/pgvectorTimescaleDB (TigerData)
November 21
News · November 213 news items

Go 1.27 Teaches go doc the @version Suffix: Inspect Package APIs Without Touching go.mod

In Go 1.27, go doc finally accepts a @version suffix on its first argument. You can now inspect a function signature or external library API right in your terminal—Go fetches the package into your local module cache without cluttering go.mod. Here are the exact commands and one key caveat.

A 16-Byte Slice Holding the Whole Buffer: Why buf[:16] in Go Blocks the Garbage Collector and How copy Fixes It

In Go, part := buf:16 doesn't copy data—it creates a slice header pointing to the exact same backing array. If you keep that tiny slice around, the garbage collector can't free the huge buffer underneath. We look at how to break that link with make and copy or slices.Clone.

Sticky Header Covering Anchor Headings? Fix It with One CSS Property: scroll-margin-top

You click a link in a table of contents, the page jumps to the section, and its heading disappears right under the sticky header. Instead of fragile negative-margin hacks or JavaScript, one line of scroll-margin-top fixes it—and a CSS variable makes it easy to adjust for mobile screens.

Paper collage showing a clean lightweight code core with redundant library layers stripped away
ArticleDevelopmentSafetyJavaScriptArchitecture

No 800 Packages in node_modules and No Heavy Electron: Three Debatable Yet Practical Principles of JS Minimalism

Long before AI coding tools, JavaScript projects were already drowning in third-party code from hundreds of transitive npm packages. In a joint stream, Timur Shemsedinov and Vlad Ten proposed three strict minimalism rules: cap dependencies at 12–30 vetted packages, swap heavy Electron wrappers for PWAs with Service Workers, and type-check plain JS with separate .d.ts files and checkJs without a build step. We show working configs, clarify the real Svelte story, and note where this approach backfires.

👍 12
HowProgrammingWorksYouTube: Тимур Шемсединов и Влад ТенSocket — Supply Chain Security for npmMDN — Service Worker API & Push API+2
November 21
Cinematic still life of a mechanical stopwatch and fanned-out indexed cards
Thematic roundup3 sectionsDevelopmentDataSQLPostgreSQL

Three Practical SQL Techniques: Speeding Up Search from 2.5s to 80ms, Index Cardinality, and Finding Duplicates with LAG

When catalog search crawls or duplicate charges show up, it's tempting to buy a bigger server or pull rows into backend code. Usually, fixing the SQL itself is easier. Here are three practical techniques with ready-to-use queries: speeding up product search 30x with a covering index, pg_trgm, and keyset pagination; why indexing a user's gender only hurts performance; and catching repeat purchases within five minutes using the LAG window function without self-joins.

👍 8
SQL Portal (оптимизация поиска)PostgreSQL Docs — Index-Only Scans and Covering Indexes
November 21
Fine engraving of a digital fingerprint woven from sound waves and geometric lines
NoteDevelopmentSafetyJavaScriptPrivacy

Browser Traces Instead of Cookies: How a Few Lines of JavaScript Build a Fingerprint Using Audio, WebGL, and SHA-256

Cleared your cookies and turned on a VPN, yet the site still recognized you? Marcin Śleszyński demonstrates how browser fingerprinting replaces third-party cookies: standard calls to OfflineAudioContext, WebGL, canvas, Intl, and navigator require zero permissions and hash via SHA-256 into a stable device ID. We walk through the minimal JS code, explain why extensions like JShelter fall short, and compare defenses in Brave, Tor, and Mullvad Browser.

👍 5
Веб-стандартыMarcin Śleszyński — Fingerprints are the new cookies (royfish.dev)EFF — Cover Your TracksMDN — SubtleCrypto.digest()
November 21
Architectural isometric mockup of five cluster nodes across three data centers with a broken quorum
NoteDevelopmentArchitectureHighloadDatabases

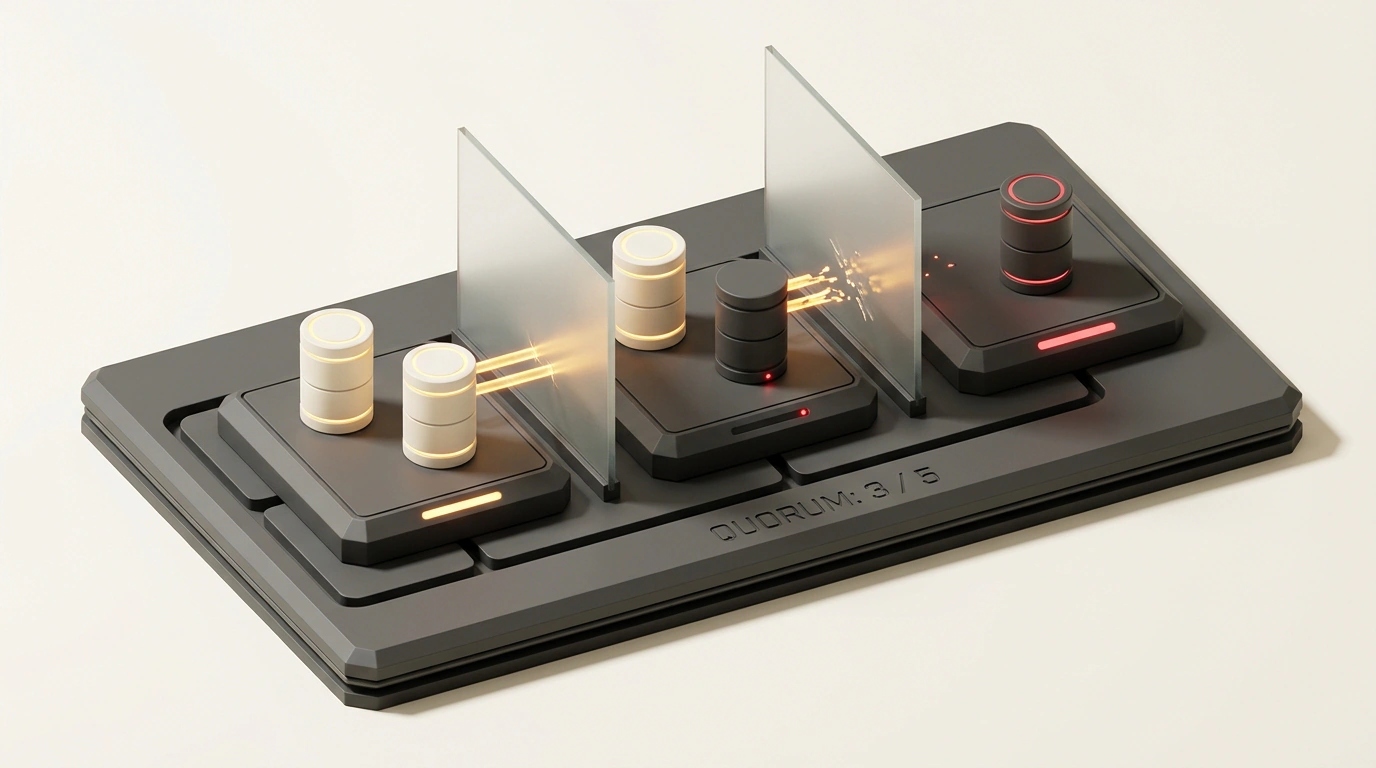
The Revolut Outage and Quorum Math: Why a 5-Node 2/2/1 Cluster Can't Survive Losing a Zone Plus One Server

A five-node cluster across three zones (2/2/1) looks rock-solid—until one server goes offline unnoticed. Using Revolut's official October 20 outage postmortem and Alexey Rybak's hypothesis about Patroni and etcd, we look at why quorum math halted automatic failover, how a dependency loop slowed recovery, and what to choose instead of 2/2/1: urgent alerting, a tie-breaker node in a fourth DC, or a 3/3/3 layout.

👍 12
System Design & HighloadRevolut Blog — 20 October Outage: Technical Overviewetcd Documentation — FAQ (Failure Tolerance)
November 21
Editorial scene in a late-night SRE office with an alert button and monitoring chart on screen
NoteDevelopmentManagementSREIncidents

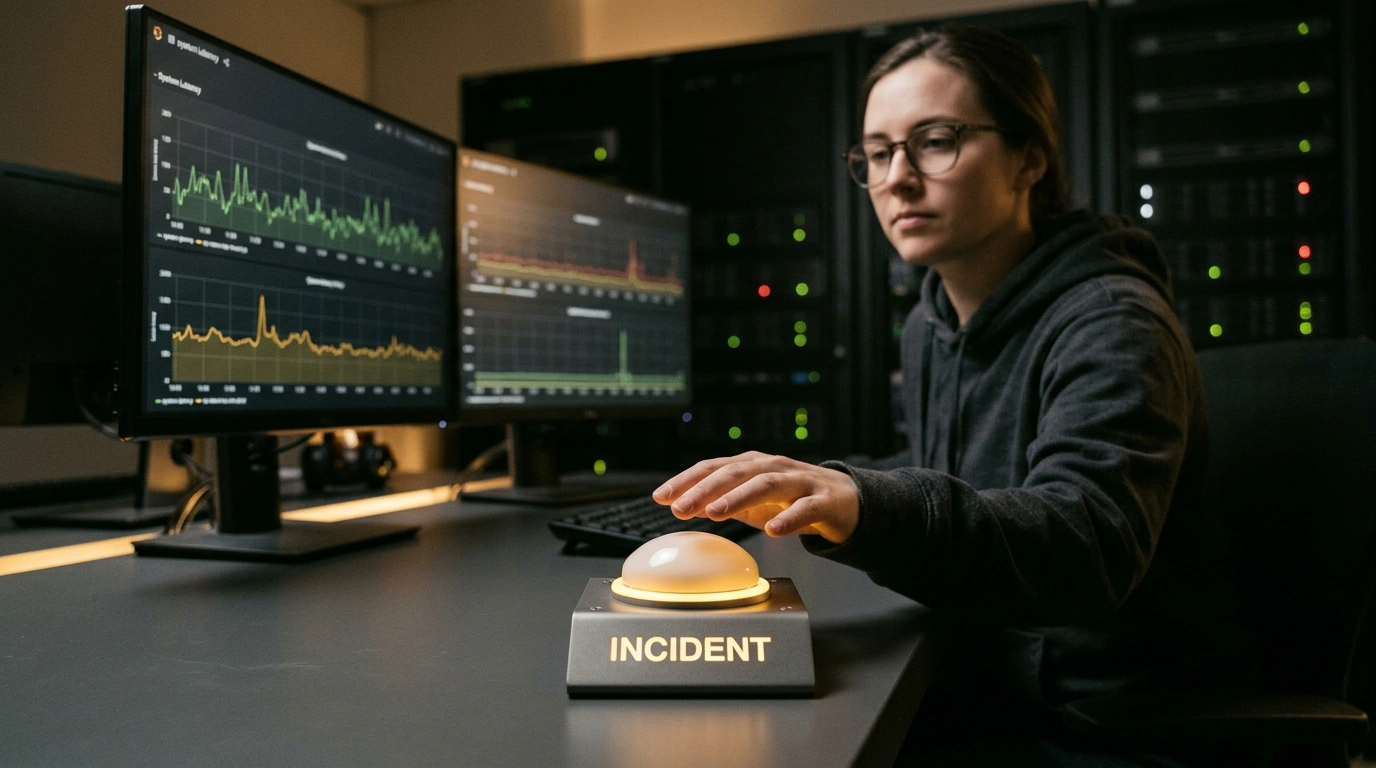
What It Costs to Declare an Incident: Why On-Call Engineers Stall and How to Make the First Step Cheap

You're on call, a chart looks weird, no alerts have fired—and you're tempted to spend ten more minutes digging through logs alone. Former Adyen SRE Hugo van der Horst explains why this isn't laziness: hitting one "Incident" button often forces an engineer to pick severity, estimate revenue loss, lead the response, and own a postmortem. That pushes teams into "shadow fixing" in DMs. Here are three rules to make starting an alert cheap, plus why separating "suspected" from "confirmed impact" matters.

👍 7
DevOps&SRE LibraryThe Postmortem (Hugo van der Horst) — What does it cost to declare an incident?Google SRE Book — Managing Incidents
November 21
AnnouncementsDevelopmentEducationPostgreSQLDevOps

Developer Event Announcements: PostgreSQL Auditing, Vibe Coding, Lakehouse Migration, and an Infra Meetup

Four upcoming events for developers and engineers between November 23 and December 11: an OTUS webinar on protecting PostgreSQL audit logs with hash chains and Merkle trees, a series of open lessons on vibe coding and auditing Cursor vulnerabilities, a VK Tech breakdown of migrating from Greenplum to a Lakehouse, and an evening meetup by AvitoTech and K2 Cloud.

👍 3
SQL и Базы ДанныхOTUS — Открытый вебинар «Журнал, который нельзя тихо переписать: hash-chain и дерево Меркла в PostgreSQL»Node.JS [ru]SQL Portal+3
November 21