People usually don't overthink security patches: bump the last digit, update the runtime on your laptop, see green tests, and ship to production. With Bun v1.4.5, released on November 19, 2026, that habit can bite you. On macOS, Bun uses the system SQLite rather than its bundled copy, so new engine restrictions won't trigger on a Mac and will only surface inside a Linux container. The same goes for corporate TLS certificates that often get bypassed locally.
What Changed Under the Hood
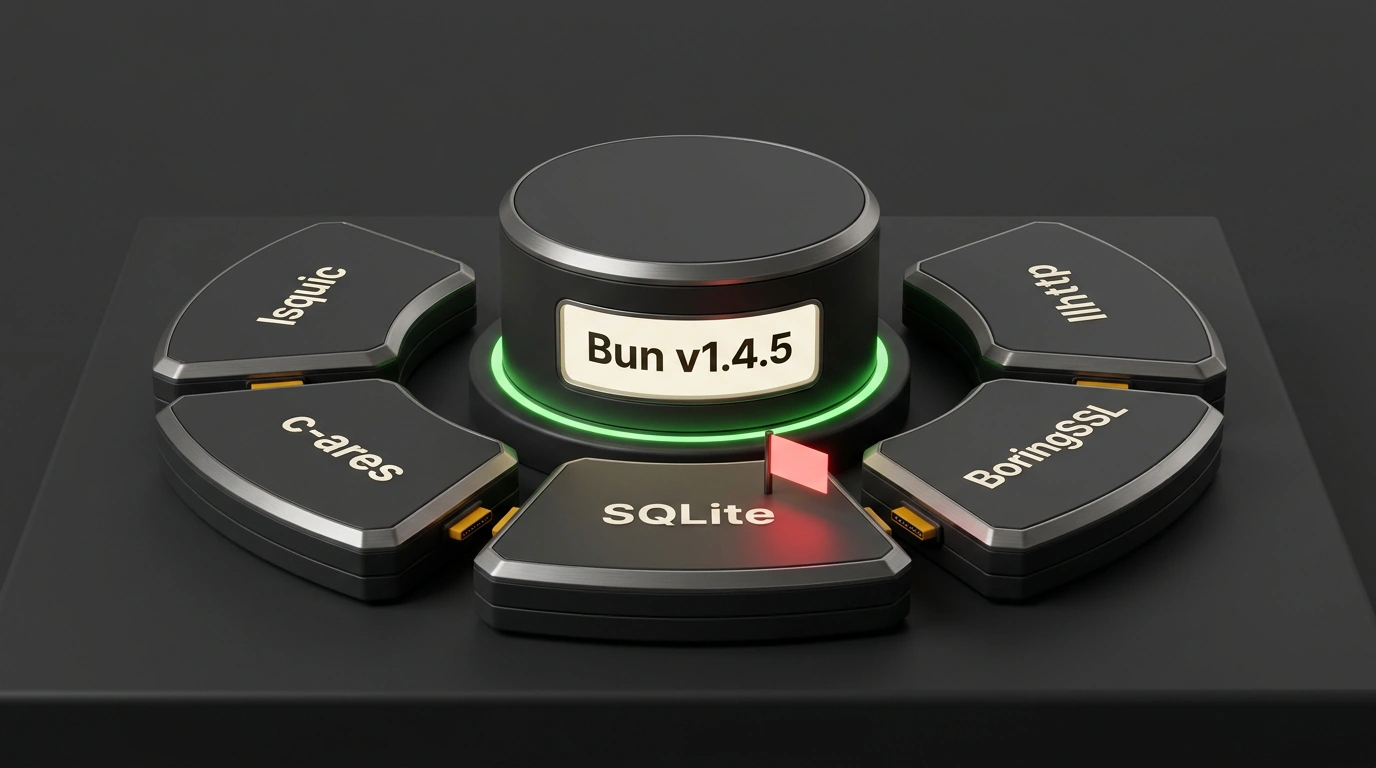
Four contributors shipped a focused, no-fluff release—the tag is already on GitHub Releases. Under the hood, five native libraries handling network traffic and the embedded database were updated.
| Library | Was (v1.4.4) | Now (v1.4.5) | Responsibility |
|---|---|---|---|
| lsquic | 4.9.4 | 4.11.2 | QUIC and HTTP/3 |
| c-ares | 1.34.8 | 1.34.9 | Asynchronous DNS |
| SQLite | 3.53.4 | 3.54.1 | bun:sqlite module |
| llhttp | 9.4.2 | 9.4.4 | HTTP/1.1 parser |
| BoringSSL | August 2026 | November 2026 | TLS and cryptography |
The update touches HTTP/3, HTTP/1.1, TLS, DNS, and Zstandard: Bun.serve, Bun.connect, Bun.dns, Bun.zstdDecompress, fetch, DecompressionStream, and Node.js modules (node:tls, node:https, node:http, node:quic, node:dns, node:zlib). Bun's authors didn't publish CVE numbers, though the SQLite changelog specifically notes a fix for a potential heap buffer overflow on 32-bit builds. They also improved HTTP/3 and node:quic stability and fixed ERR_OSSL_RSA_UNKNOWN_ALGORITHM_TYPE in node:crypto for RSA signatures with SHA-3, SHA-512/224, SHA-512/256, and RIPEMD-160.
Two Places Where the Upgrade Can Bite
If your service uses standard Bun root certificates and doesn't touch SQLite system columns, the upgrade will go unnoticed. You should pause and check in two cases.
First is the built-in bun:sqlite on Linux and Windows. The new engine forbids ALTER TABLE from adding, renaming, or dropping rowid, oid, or _rowid_ columns (hidden row identifiers). Also, the setAuthorizer() permission callback now fires for SQL functions inside DEFAULT expressions.
import { Database } from "bun:sqlite";

const db = new Database(":memory:");
db.run("CREATE TABLE logs (msg TEXT)");

// On Linux and Windows in SQLite 3.54+, this migration will fail:
// rowid, oid, and _rowid_ are now forbidden in ALTER TABLE
db.run("ALTER TABLE logs ADD COLUMN oid TEXT");

// Functions in DEFAULT are now also checked by setAuthorizer()
db.run("CREATE TABLE events (at TEXT DEFAULT (datetime('now')))");
If legacy migrations have an oid column or a strict setAuthorizer(), everything will pass quietly on a Mac thanks to system SQLite, then crash on startup in a Linux Docker container.
The second catch is custom root certificates. Validation is stricter now, so some older corporate CAs are rejected (Bun's built-in roots are unaffected). node:tls behavior now matches Node.js: an expired certificate from an unknown issuer returns CERT_HAS_EXPIRED, and allowPartialTrustChain combined with crl (certificate revocation list) now requires a self-issued root at the end of the chain.
import tls from "node:tls";

// Test on staging: older custom CAs may be rejected,
// and crl + allowPartialTrustChain require a self-issued root
const socket = tls.connect({
  host: "internal.example.local",
  port: 443,
  ca: customRootCaPem,
  crl: customCrlPem,
  allowPartialTrustChain: true,
});
Settings like these often live in internal integrations or Bun.serve with client certificates. It's much easier to test them on staging ahead of time than to debug TLS drops after a late-night deploy.
How to Upgrade and Verify Your Project
For an existing environment, one command is enough; for CI or a fresh machine, use the official install scripts.
# Upgrade an existing Bun installation
bun upgrade

# Fresh install on Linux / macOS
curl -fsSL https://bun.com/install | bash

# Fresh install on Windows (PowerShell)
powershell -c "irm bun.com/install.ps1|iex"

# Verify the installed version
bun --version
After upgrading, don't stop at Mac tests if you deploy to Linux. Running through the short checklist below will catch every release surprise.
What to Check Before Rolling Out to Production
- Upgrade Bun locally and in Docker to
1.4.5and verifybun --version. - Run
bun:sqlitemigrations inside a Linux container to catch forbiddenALTER TABLEstatements andsetAuthorizer()calls inDEFAULT. - Test TLS connections using corporate CAs,
crl, andallowPartialTrustChain. - Remove
ERR_OSSL_RSA_UNKNOWN_ALGORITHM_TYPEworkarounds if you use RSA with SHA-3 or RIPEMD-160 innode:crypto.