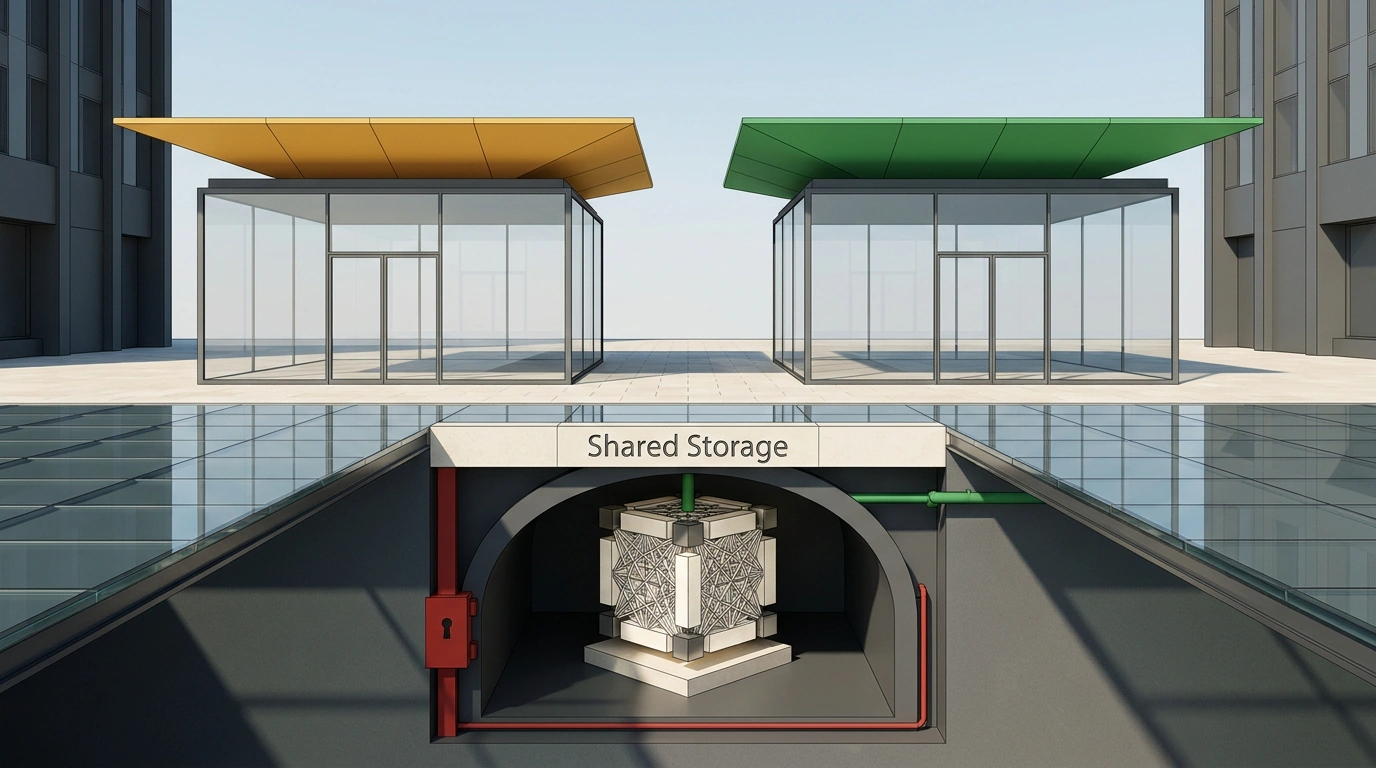
Two web apps load the exact same multi-gigabyte Gemma model. Why does the browser download it twice and store a second copy?
Why Shared CDNs Stopped Saving Bandwidth
Years ago, loading a font from a shared CDN meant pulling it straight from the browser cache across sites. Trackers abused that shortcut: using a cache-timing attack, a third-party site could measure how fast a rare file loaded and infer which sites you had visited.
Browsers responded with cache partitioning, splitting the HTTP cache by top-level site. Privacy improved, but shared savings vanished: two cross-origin sites using the same CDN file now download and store separate copies.
For a 100 KB script, that was tolerable. Local AI models (Gemma, Llama, Whisper) run into gigabytes, alongside heavy Wasm runtimes (Flutter, Godot, Unity) and web fonts. Re-downloading them on every site wastes bandwidth and SSD space.
On November 10, 2026, Thomas Steiner, Christian Liebel, and François Beaufort from Chrome introduced the Cross-Origin Storage API (COS) in the WICG, the W3C's incubator for new web standards.
How the Cross-Origin Storage API Works in Code
COS is built around content-addressable storage. Instead of a URL, the key is the hash of the file's bytes (SHA-256 and other Web Crypto algorithms, excluding SHA-1). It stores only raw bytes—no URLs, MIME types, or headers—so identical files from different servers map to the same slot.
The API builds on FileSystemFileHandle from the File System Standard:
// Key a file by the hash of its bytes
const modelHash = {
  algorithm: 'SHA-256',
  value:
    '8f434346648f6b96df89dda901c5176b' +
    '10a6d83961dd3c1ac88b59b2dc327aa4',
};

async function loadModel(url) {
  try {
    // 1. Check for an existing file in shared storage
    const h = await navigator.crossOriginStorage.getFileHandle(modelHash);
    return await h.getFile();
  } catch (err) {
    if (err.name !== 'NotFoundError') throw err;

    // 2. Cache miss — fetch and store it
    const blob = await (await fetch(url)).blob();
    const h = await navigator.crossOriginStorage.getFileHandle(modelHash, {
      create: true,
      origins: ['https://app-b.example'],
    });
    const out = await h.createWritable();
    await out.write(blob);
    // Verifies SHA-256 on close() or throws DataError
    await out.close();
    return blob;
  }
}
On a cache miss, getFileHandle() throws NotFoundError and your code falls back to the network. On close(), the browser verifies the SHA-256 hash and throws DataError if the bytes don't match. In-progress writes stay hidden from other tabs, and disk space is bounded by quota (QuotaExceededError).
To avoid boilerplate, the proposal plans four integrations on top of integrity: a crossoriginstorage HTML attribute, a JS import attribute, CSS cross-origin-storage(), and a fetch() option (GET only):
// Planned Wasm loading via fetch() and COS
const { instance } = await WebAssembly.instantiateStreaming(
  fetch('https://cdn.example/runtime.wasm', {
    integrity: 'sha256-abc123...',
    crossOriginStorage: { origins: '*', contentType: 'application/wasm' },
  }),
  imports,
);
The call checks the hash-keyed cache first and hits the CDN only on a miss. Details like contentType are still under discussion, but the goal is minimal code.
What About Tracking, and When Can You Use It?
An obvious question pops up: if a site can ask "do you have a file with this hash?", didn't we just bring tracking back?
In the WICG privacy review, three layers close that hole. By default, a stored file is visible only to its own site (same-site). Passing an explicit origins list requires a Cross-Origin-Storage-Allow-Origin header from the server hosting the bytes, so even XSS can't leak a private file.
Global origins: '*' works only through a Public Hash List (PHL)—an open registry of hashes for popular public models and fonts. If a hash isn't on the list, another site gets NotFoundError. On top of that sit GREASE'ing (occasional fake NotFoundError responses that spoil tracking and keep fallbacks tested) and lookup rate limits.
It's too early for production: this is an early WICG draft and an Intent to Prototype on Chrome Platform Status, with no Origin Trial yet. Positions from Mozilla, WebKit, and the W3C TAG have been requested, and WebKit historically takes a hard line against cross-site channels.
You can already experiment with it via a polyfill extension for Chrome, Firefox, and Safari, plus vite-plugin-cross-origin-storage. Behind flags, teams are already testing it in Transformers.js, WebLLM, wllama, Flutter, Emscripten, and Nuxt.js.

