What actually holds up the modern internet? Strip away the trendy frontend frameworks and cloud microservices, and underneath the vast majority of public websites you will find good old PHP. It powers WordPress, Drupal, Magento, thousands of online stores, and government portals—more than 70% of web servers on the planet.
After three decades, you would assume the C codebase of the PHP interpreter had been scrubbed spotless. Static analyzers (SAST) scan it around the clock, AFL++ fuzzers hammer it nonstop, and top security researchers audit it constantly. Finding a fundamental zero-day flaw there sounded like science fiction.
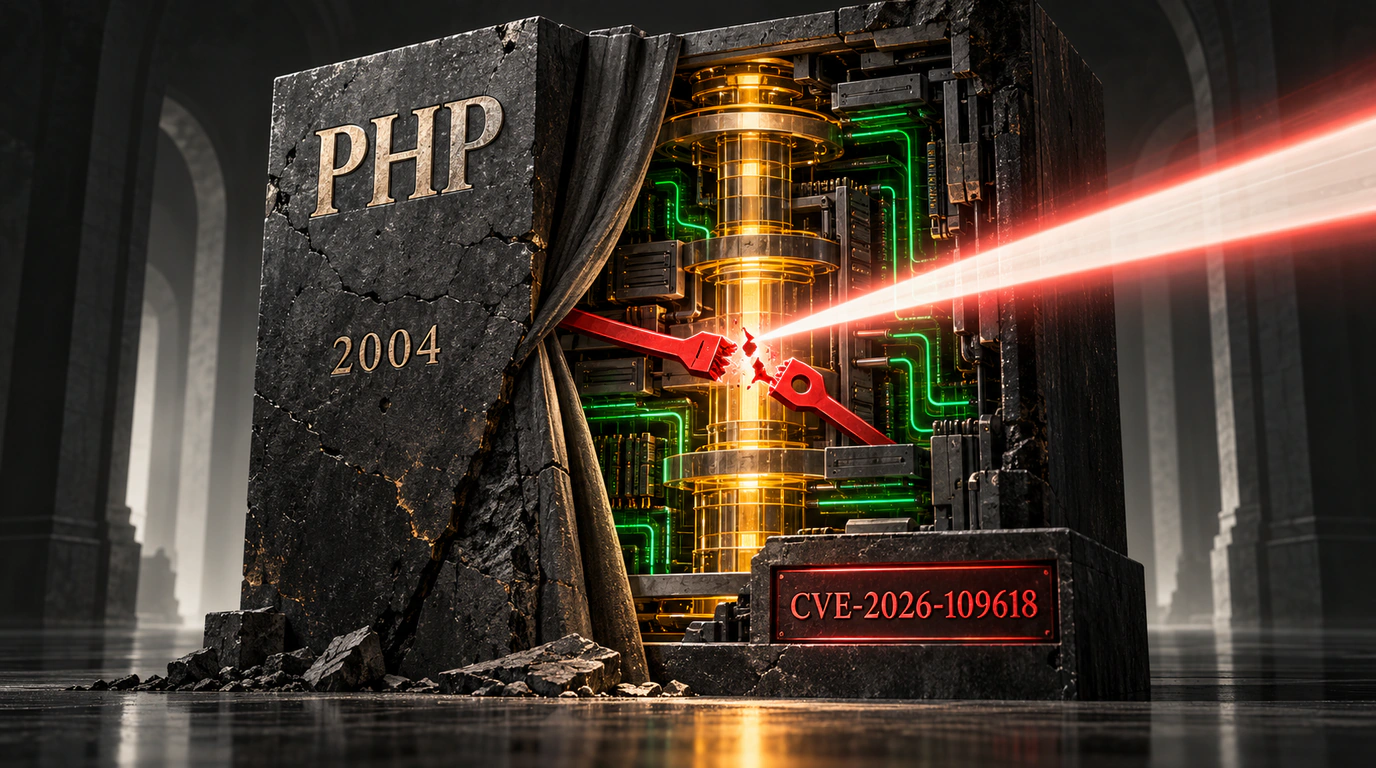
Yet on October 21, 2026, the PHP Foundation issued an emergency security advisory. Working under the "Patch the Planet" initiative, researchers from Calif and Wiz—assisted directly by OpenAI reasoning models (the GPT-5.6 Sol / o-series family)—uncovered a pair of critical PHP2Shell vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619, carrying a severe CVSS 9.2 rating.
Anatomy of the Flaw: A Ghost from 2004
The most astonishing detail in this story is the age of the bugs. The vulnerable code had been sitting quietly inside PHP's core repository since 2004—over twenty years! Traditional code scanners missed it because the flaw only triggered under a very specific sequence of rare system events.
Engineering blueprint of a RAM map highlighting an isolated freed Use-After-Free block and a dangling pointer
What was the bug? It is a classic Use-After-Free (UAF) memory error—accessing a pointer in RAM after the operating system has already freed that block of memory:
CVE-2026-109618: the flaw lived in the upload-progress unserializer. If a client dropped the connection at a precise moment during an HTTP request body transfer, the memory was freed while a cached frame descriptor remained readable;CVE-2026-109619: a companion bug involving OPcache type confusion when building a backtrace during a fatal out-of-memory (OOM) error.
Paired with Apache and mod_php, an attacker could craft a malicious HTTP request that achieved Unauthenticated Remote Code Execution (RCE). Worse still, the payload executed inside the web server's address space before any PHP application-level access checks even ran.
We looked at how web code execution environments are evolving in Evolution of Web Browsers: From Page Viewers to an Operating Environment for AI Agents.
Why Reasoning Models Spotted What Humans Missed
How did a language model crack a problem that automated fuzzers failed to catch for twenty years? Conventional static analyzers match patterns—flagging unsafe calls like strcpy or obvious leaks—but they cannot hold the state of a complex asynchronous call chain across ten layers of abstraction.
Reasoning models operate differently. They mentally emulate C execution step by step, tracking heap pointer states through failure paths:
- The model asked itself: "What happens to the trace struct if
free_memory_pool()runs right in the middle of handling an OOM signal?" - Tracing the execution graph, it spotted the dangling pointer dereference;
- And it immediately generated a reproducible Proof of Concept (PoC) confirming the exploit.
We examined the architecture behind deep reasoning systems in The Dot Platform and OpenAI DevDay Announcements: Moving Toward Autonomous Work Agents.
Take a look at a simplified view of the vulnerable core block and the official patch:
/* Vulnerable PHP core snippet (pre-patch logic) */
void php_handle_fatal_error(php_backtrace_t *trace) {
    if (trace->state == OUT_OF_MEMORY) {
        free_memory_pool(); // Free the memory pool
        // CRITICAL BUG: reading from an already freed address (UAF)
        log_backtrace_details(trace->cached_frame);
    }
}

/* Patched safe snippet (PHP Foundation fix) */
void php_handle_fatal_error_patched(php_backtrace_t *trace) {
    if (trace->state == OUT_OF_MEMORY) {
        // Copy critical data to an isolated stack buffer before freeing the heap
        php_safe_frame_t safe_frame;
        copy_frame_to_static_buffer(&safe_frame, trace->cached_frame);

        free_memory_pool();
        log_backtrace_safe(&safe_frame); // Safe logging
    }
}
What System Administrators Must Do Right Now
The PHP Foundation shipped patches promptly for all supported interpreter branches: PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
Check your server's PHP version right in the terminal:
php -v
# Output should match a patched release built after October 21, 2026:
# PHP 8.4.27 (cli) (built: Oct 21 2026 14:02:10)
If you cannot upgrade PHP binaries this instant, immediately migrate servers off the legacy mod_php module to Nginx + php-fpm with process isolation and a strict memory_limit, or enable Cloudflare WAF rules that block malformed deserialization requests.
A reasoning model's ability to uncover 20-year-old zero-days in infrastructure software is both a shield and a weapon. If defenders use these algorithms to harden code, attackers will inevitably use them to synthesize exploits automatically. Patching speed in 2026 is a matter of business survival.
The PHP2Shell discovery sends a clear signal across the industry: critical infrastructure security auditing is shifting from manual review to large-scale autonomous AI scanners.